5-step SRA-compliant framework
An AML incident log template UK law firms implement is a centralized register that documents compliance breaches, suspicious activity identification, and corrective actions. The SRA expects UK law firms to maintain this record to demonstrate governance and prove self-reporting of serious breaches.
This guide shows how to build an AML incident log template UK law firms can use to meet regulatory expectations and simplify SRA examinations.
What is an AML incident log template UK law firms use?
An AML incident log template that UK law firms implement is a centralized register documenting compliance incidents, breaches, and near-misses. It records failed CDD procedures, SAR submission delays, customer identification errors, beneficial ownership gaps, and sanctions screening failures.
The AML incident log template provides evidence to the SRA that your firm identifies risks and takes corrective action during desk-based reviews and inspections.
Why AML incident log template documentation matters for UK firms
The SRA expects firms to self-report serious breaches. An AML incident log template demonstrates the following: incidents are identified and documented (firms without records face sanctions), root causes are investigated (not generic “isolated incident” explanations), corrective action is tracked (self-reported breaches with remediation receive lower penalties), and systemic issues trigger firm-wide training or policy updates.
Regulatory framework: UK AML incident log requirements
The Money Laundering, Terrorist Financing, and Transfer of Funds (Information on the Payer) Regulations 2017 (MLR 2017) set baseline AML requirements for law firms. The LSAG Guidance (effective April 2025) provides official interpretations. The SRA’s AML Topic Guide and breach reporting guidance specify that serious breaches must be reported to the SRA within a reasonable period.
Serious breach categories requiring AML incident log documentation:
Intentional or reckless MLR 2017 violations. Systemic regulatory failures (multiple incidents, weak controls). Breaches indicating money laundering facilitation risk. One-off breaches of limited scope need not be reported to the SRA but must be logged and remediated per SRA guidance.
Building an AML incident log template
5 essential elements:
Element 1: Incident identification and classification
Record incident date, discovery date, incident type (CDD failure, late SAR, screening gap), area affected, and severity (critical, high, medium, low).
Element 2: Detailed description
Document what went wrong. Example: “Failed to obtain source-of-funds documentation for conveyancing matter >£500k; CDD complete but SoF section blank; discovered during MLRO monthly review.”
Element 3: Root cause analysis
Identify why the breach occurred: staff undertrained, system misconfigured, procedure unclear, supervision gap, conflicting guidance misunderstood.
Element 4: Corrective action taken
Record what fixed the immediate issue (re-obtained documentation, resubmitted SAR, escalated to MLRO), date taken, and evidence of completion.
Element 5: Preventive action and monitoring
Document systemic changes to prevent recurrence: a procedure rewritten, staff retrained, and a system reconfigured. Include follow-up review dates to confirm effectiveness.
AML incident log template: Sample table
| Date Identified | Incident Type | Client/Matter | Description | Severity | Root Cause | Corrective Action | Preventive Measure | Resolved Date | MLRO Sign-Off |
|---|---|---|---|---|---|---|---|---|---|
| 15/01/2026 | CDD Failure | Acme Corp M&A | Source-of-funds section of CDD form blank; only identity verified | High | Staff misunderstood “simplified CDD” scope; thought SoF not required for corporate M&A | Contacted client, obtained missing SoF documentation within 5 days | Rewrote CDD procedure with flowchart distinguishing simplified vs full CDD; retrained fee-earning team | 22/01/2026 | J. Smith MLRO 23/01/26 |
| 08/02/2026 | SAR Delay | Private Client Estate | Suspicious transaction pattern: 6 x £9,900 transfers in 2 weeks; SAR due but not submitted within 5 days of suspicion | Critical | The MLRO was unaware of suspicious transactions; transaction monitoring alerts went to fee earner only and were not escalated | Fee earner reported to MLRO; SAR filed 3 days late with Proceeds of Crime Act 2002 notification | Procedure revised: transaction alerts >£5k now auto-copy to MLRO; monthly MLRO review of all alerts >£5k added | 15/02/2026 | J. Smith MLRO 16/02/26 |
| 22/02/2026 | Beneficial Ownership Gap | Conveyancing | Corporate buyer: directors identified but no UBO verification; should have identified true beneficial owners under MLR 2017 | Medium | Procedure assumed directors = beneficial owners; UBO register check not performed | Obtained UBO register extract; verified true owners, and file updated | CDD template updated to mandate UBO register check for all corporate clients; staff briefing conducted | 01/03/2026 | J. Smith MLRO 02/03/26 |
Best practices for AML incident logging
Log incidents in real time. Incident logs must be contemporaneous to demonstrate governance. Monthly or post-inspection backfilling appears evasive and raises SRA concerns.
Use consistent terminology. Define “incident” vs. “breach” vs. “near-miss” in firm procedures. One firm’s incident may be another’s breach; consistency makes SRA enforcement assessments fair.
Ensure MLRO sign-off. Every entry should be reviewed and signed by the MLRO or MLCO. This proves senior oversight and strengthens the self-reporting narrative.
Distinguish systemic vs. isolated. One data-entry error is isolated; three similar errors in six months is systemic. The SRA differentiates when calculating enforcement action.
Link to training and procedure updates. Reference training records and updated procedure versions by date. This proves remediation was substantive, not superficial.
Common incidents in UK law firms
CDD documentation gaps. Identity is verified, but beneficial ownership is incomplete. The source of funds for high-value transactions is missing. High-risk client classifications were not assigned when jurisdiction red flags existed.
SAR submission delays. Suspicious transactions were identified, but an SAR was not filed within the required timeframe. The MLRO was unaware of red flags due to failed escalation procedures. “Tipping off” risk created by premature client communication.
Sanctions and PEP screening failures. Customer screened once at onboarding but not rescreened when risk profile changed. OFAC match overlooked. Outdated screening results relied upon.
Scope misclassification. Work was treated as out of scope when it fell within the MLR 2017 scope. Example: Conveyancing over £15k is treated as “low-risk” with simplified CDD instead of full CDD per SRA guidance.
Supervision gaps. Work carried out without fee-earner understanding AML obligations. New staff are not trained before handling in-scope work. The MLRO is not given timely visibility of suspicious transactions.
How technology supports AML incident log template implementation
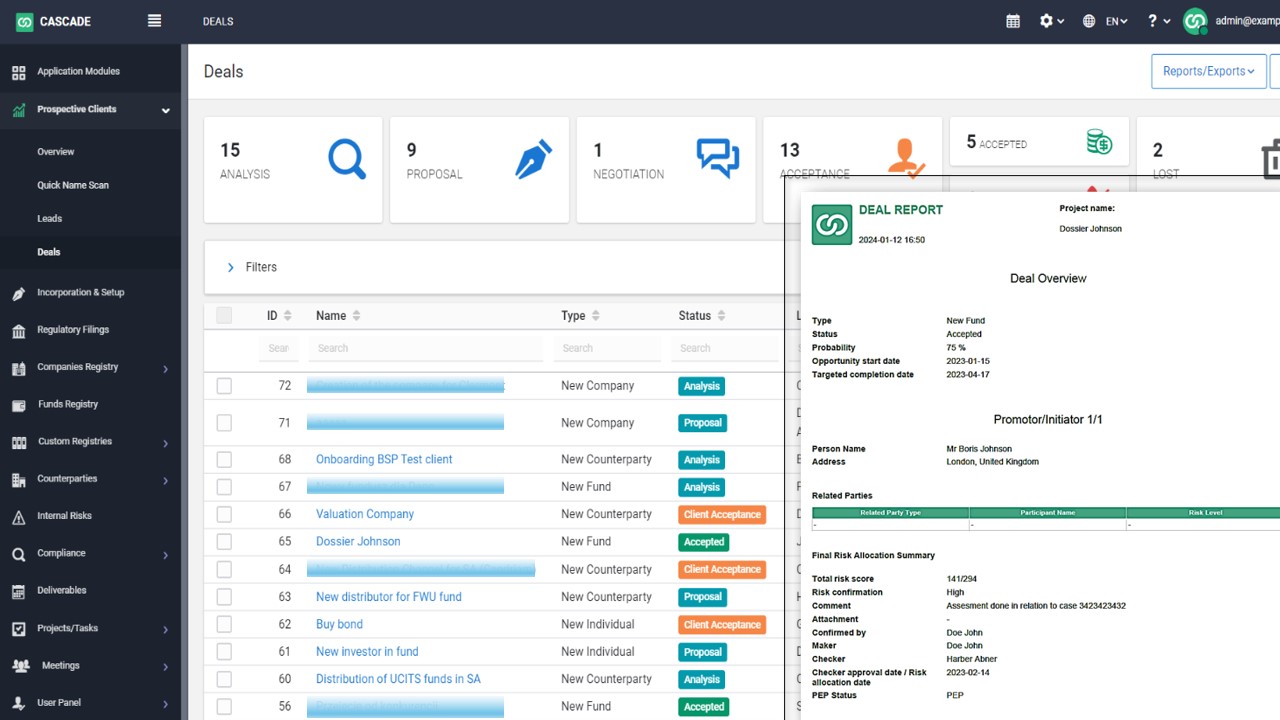
Automated alerts flag CDD gaps and late SAR submissions in real time. Workflow systems route incidents to MLRO for review and sign-off. Audit trails record when incidents were logged and any updates. Integration with screening tools links incidents to client matters and corrective actions.
Yes, Cascade’s AML Software can potentially support UK law firms with structured AML incident logging and related compliance workflows, subject to their specific requirements.
Schedule a demo with our compliance team.
FAQs
Should we report one-off data-entry errors to the SRA?
No. One-off, limited-scope errors need not be reported—log and remediate them. If the same error recurs, the pattern becomes systemic and requires SRA reporting.
How long should we retain AML incident log records?
Retain for six years post-closure of the related client matter, minimum. This aligns with MLR 2017 record retention requirements.
What if an incident reveals an earlier breach we missed?
Document the incident with the discovery date and root cause; note when the breach occurred. Early self-report is a mitigating factor with the SRA.
Does Cascade help UK law firms with AML incident logging?
Yes, Cascade’s AML Software can potentially support UK law firms with structured AML incident logging and related compliance workflows, subject to their specific requirements.
Can we use a spreadsheet for the incident log?
Spreadsheets lack audit trails. The SRA prefers centralized, access-controlled systems. They are acceptable for small firms; larger firms should migrate to compliance software.
What constitutes a “serious” breach requiring SRA reporting?
Intentional/reckless MLR 2017 violations, systemic procedural failures, or breaches indicating money laundering facilitation risk. Contact the SRA confidentially when in doubt.
Disclaimer
This article is for general information only and not legal or compliance advice. MLR 2017 requirements vary by firm size and service scope; consult your MLRO, legal team, or external counsel to tailor this framework to your firm. The template is illustrative. Examples do not guarantee SRA acceptance or compliance. Your firm remains responsible for identifying, reporting, and remediating AML incidents in accordance with MLR 2017 and SRA expectations. Cascade does not provide legal advice and does not guarantee regulatory compliance or immunity from SRA enforcement. Compliance accountability remains with your firm.


 English
 English (Australia)
 English (UK)