Measuring compliance performance
This guide explains the key performance indicators that Irish fund administrators must track to measure AML compliance effectiveness. You’ll learn which metrics matter most, how to benchmark performance, and how to embed KPI monitoring into your governance framework. By the end, you’ll have a practical framework for monitoring AML KPIs for fund administrators in Ireland across onboarding, screening, and ongoing customer risk assessment.
Introduction
Fund administrators in Ireland face rising regulatory scrutiny around AML/KYC performance. The Central Bank of Ireland and the Financial Intelligence Unit now expect firms to demonstrate measurable compliance outcomes, not just process completion. This guide sets out the AML KPIs you need to track to stay ahead of regulatory expectations and reduce financial crime risk.
Whether you manage €10m or €10bn in assets, AML KPIs for fund administrators in Ireland form the backbone of your compliance argument. They show regulators and your board that you’re managing financial crime risk actively, not just ticking boxes.
What are AML KPIs for fund administrators?
AML KPIs are measurable compliance metrics that track the effectiveness of your anti-money laundering programme. For fund administrators, these span customer onboarding timeliness, screening hit rates, customer risk reassessment frequency, and sanctions compliance. They convert vague compliance mandates into numbers you can report, trend, and act on.
AML KPIs for fund administrators in Ireland must align with POCA 2010, the Criminal Justice Act 2011, and Central Bank guidelines on risk-based AML governance. The Irish regulator expects fund administrators to define what good looks like, set realistic targets, and report performance quarterly.
Why AML KPIs matter for Irish fund administrators
Regulatory expectation is the obvious driver. The Central Bank’s 2024 AML/CFT thematic reviews highlighted poor KPI governance as a persistent deficiency. Firms without clear metrics struggle to explain compliance decisions to examiners. That’s both a compliance and reputational risk.
Beyond regulation, KPIs unlock operational insight. They reveal bottlenecks in onboarding, false positive trends in screening, and patterns in customer risk downgrades. Without measurement, compliance teams work blind. With it, you prioritize resources where they matter most.
Regulatory framework for fund administrators in Ireland
The Central Bank of Ireland requires fund administrators to implement AML controls proportionate to customer risk. POCA 2010 mandates customer due diligence; the Criminal Justice Act 2011 expanded beneficial ownership and PEP screening requirements. Both statutes are silent on specific KPIs, but the Central Bank’s expectations guidance makes clear that you must define, measure, and report performance.
Relevant frameworks: CSSF (cross-border); ECB guidance on governance and risk; ESMA guidelines on product governance (applicable to fund managers and administrators); and the Irish Central Bank’s own AML/CFT supervision handbook.
Core AML KPIs for fund administrators
Essential metrics include the following:
- Onboarding completion time (target: 95% within 10 business days)
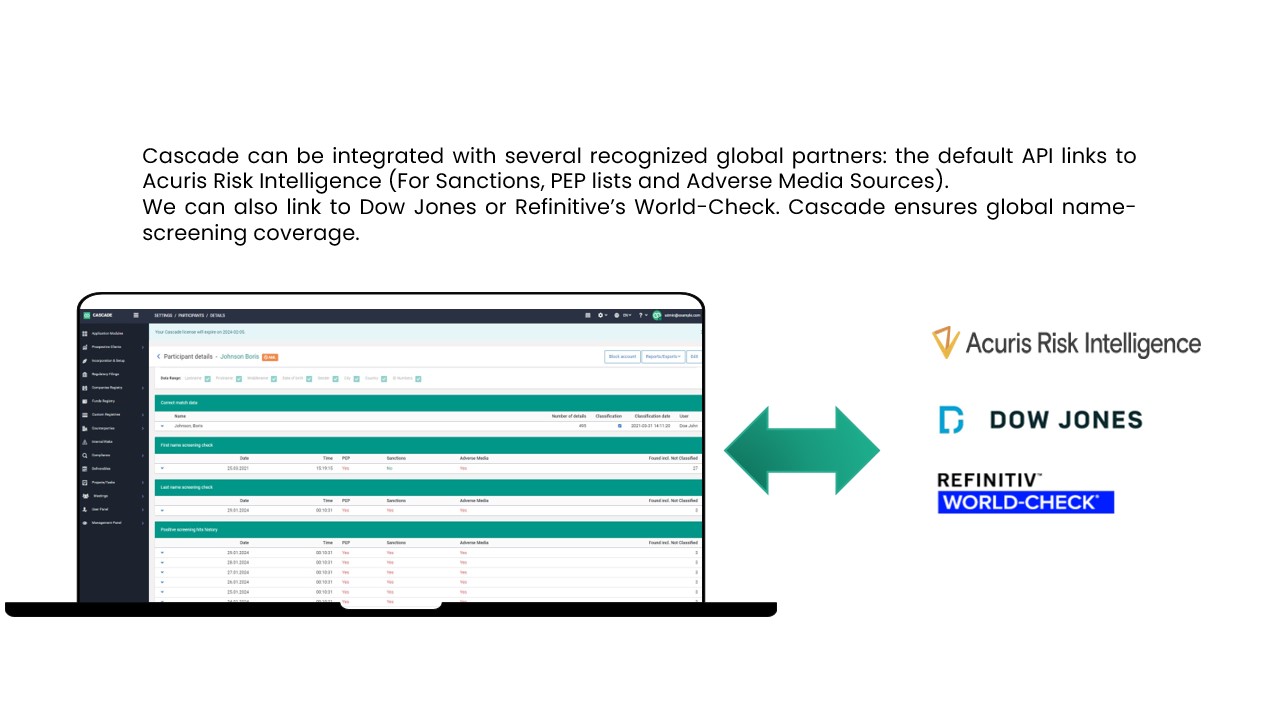
- Customer screening timeliness (target: 100% screened on day 1)
- Hit rate and false positives (typical range: 0.5–2%)
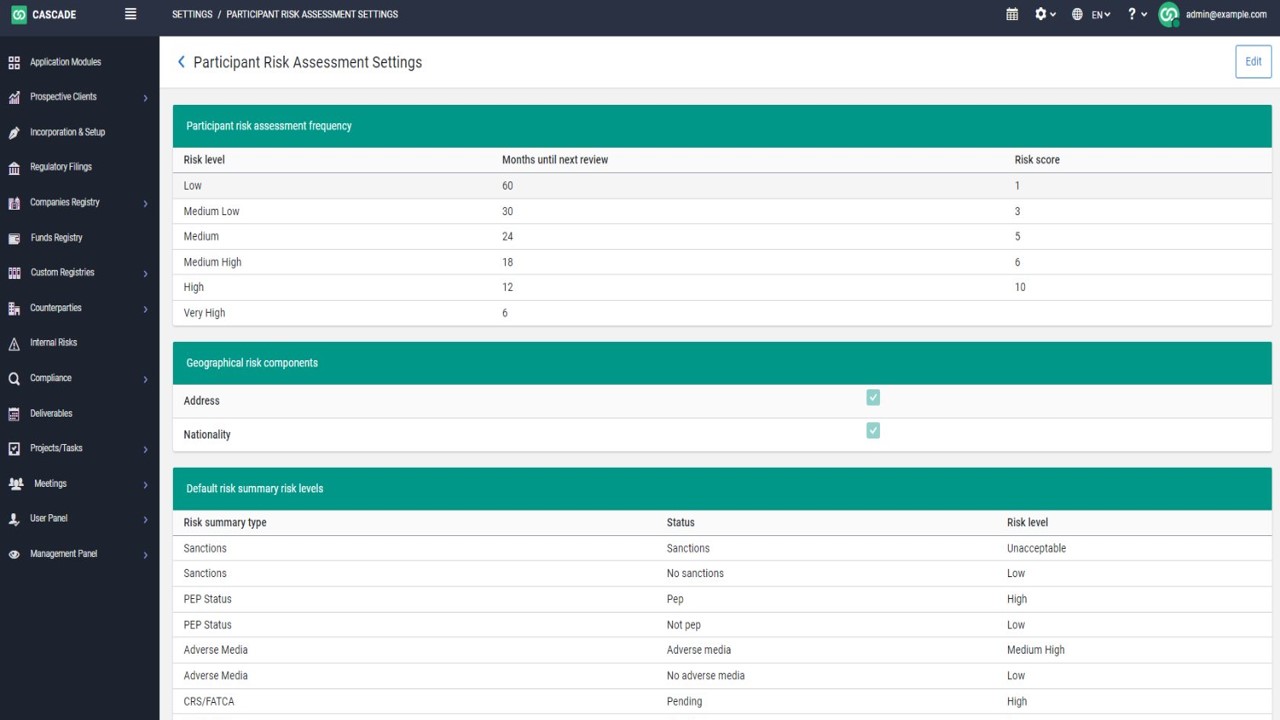
- Customer risk reassessment frequency (target: 100% annually for high-risk)
- Sanctions compliance rate (target: 100% no breaches)
- EDD completion ratio (target: 100% where risk warrants)
- Training completion and test pass rates (target: 100% annually)
Document each target, rationale, and responsible owner. Review quarterly with compliance and board governance committees.
Common compliance gaps
Fund administrators often confuse process metrics (e.g., documents received) with outcome metrics (e.g. customer risk correctly classified). They set targets that are too generous or too strict. They fail to segment KPIs by customer risk tier, missing the value of risk-based proportionality. They also lack data integration, manually collating figures from disparate onboarding, screening, and CRM systems.
Best practices for AML KPI governance
Define KPIs in writing with clear calculation methodologies. Assign ownership and accountability. Use a risk-based approach: stricter targets for high-risk customers and jurisdictions. Benchmark against peers and regulatory expectations. Review monthly operationally; report quarterly to governance. Investigate and document variances. Integrate data where possible to reduce manual work and error.
How technology can help
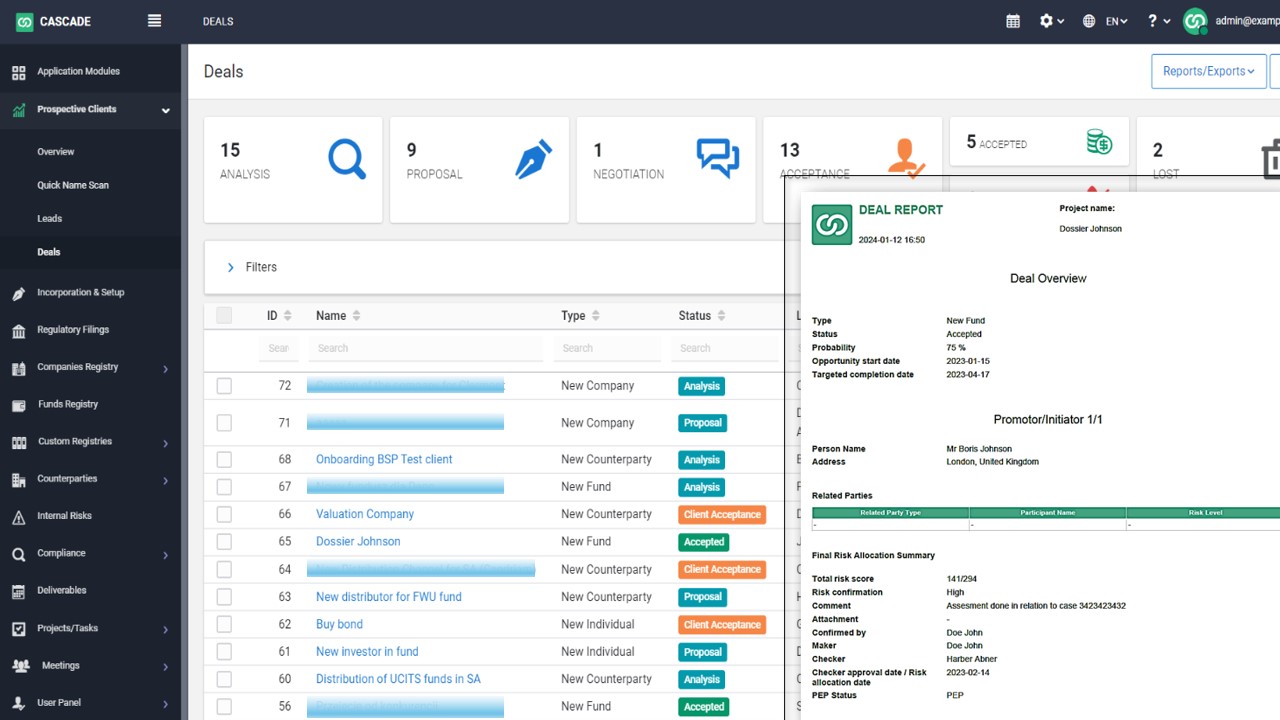
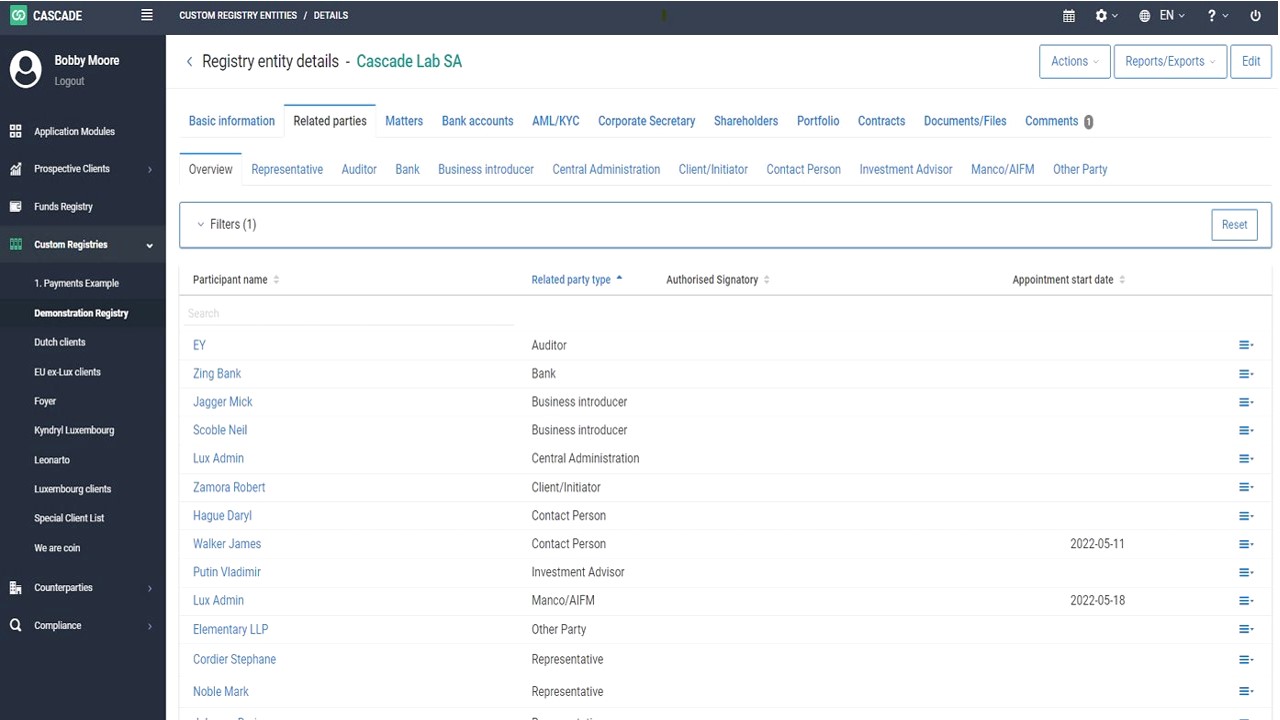
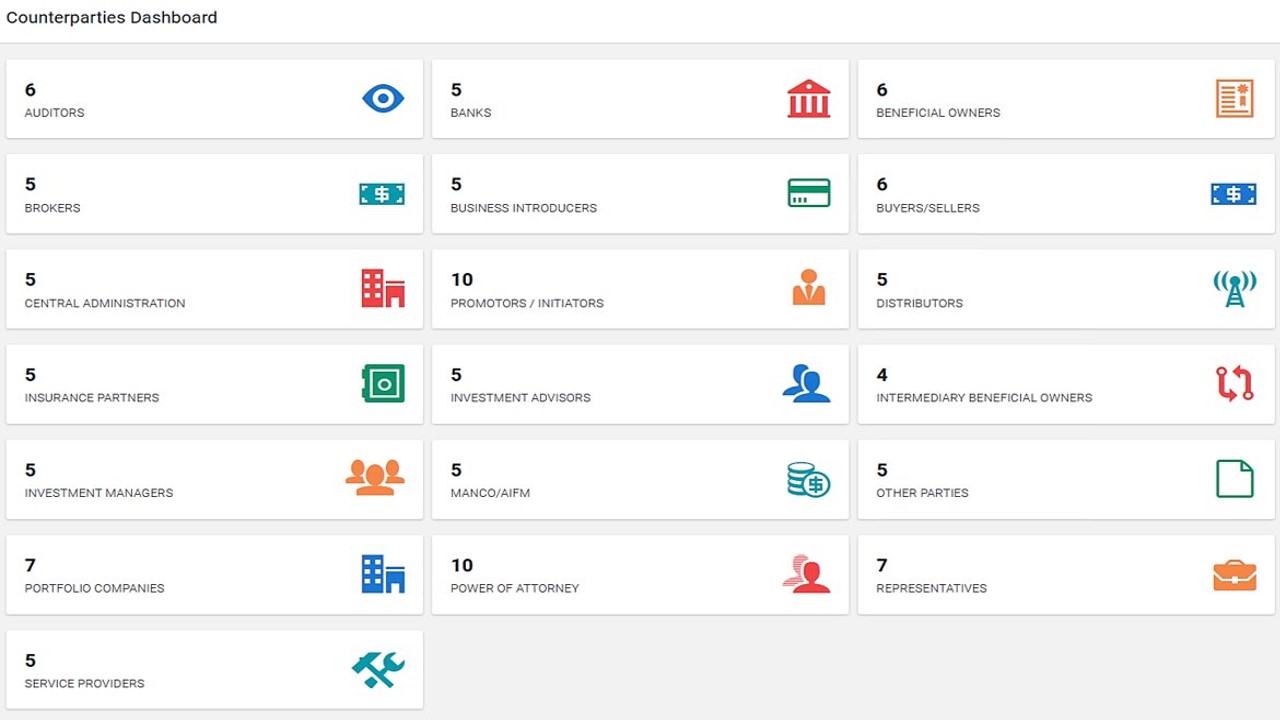
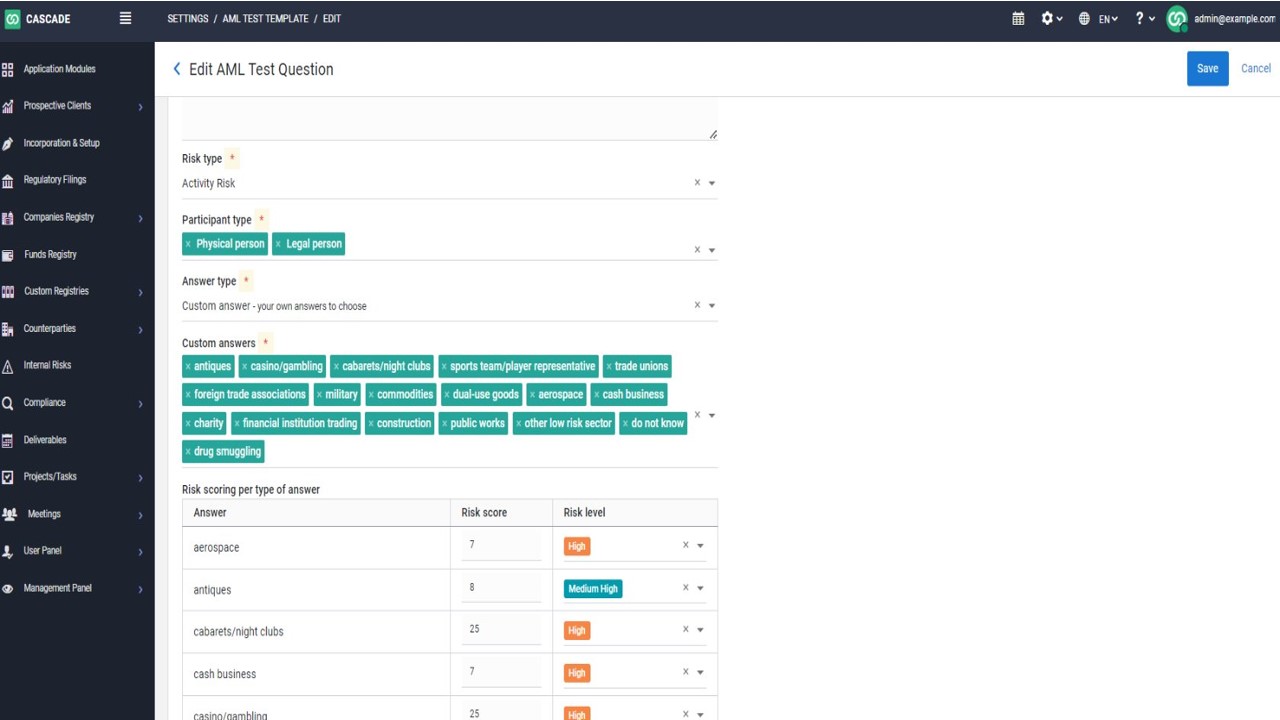
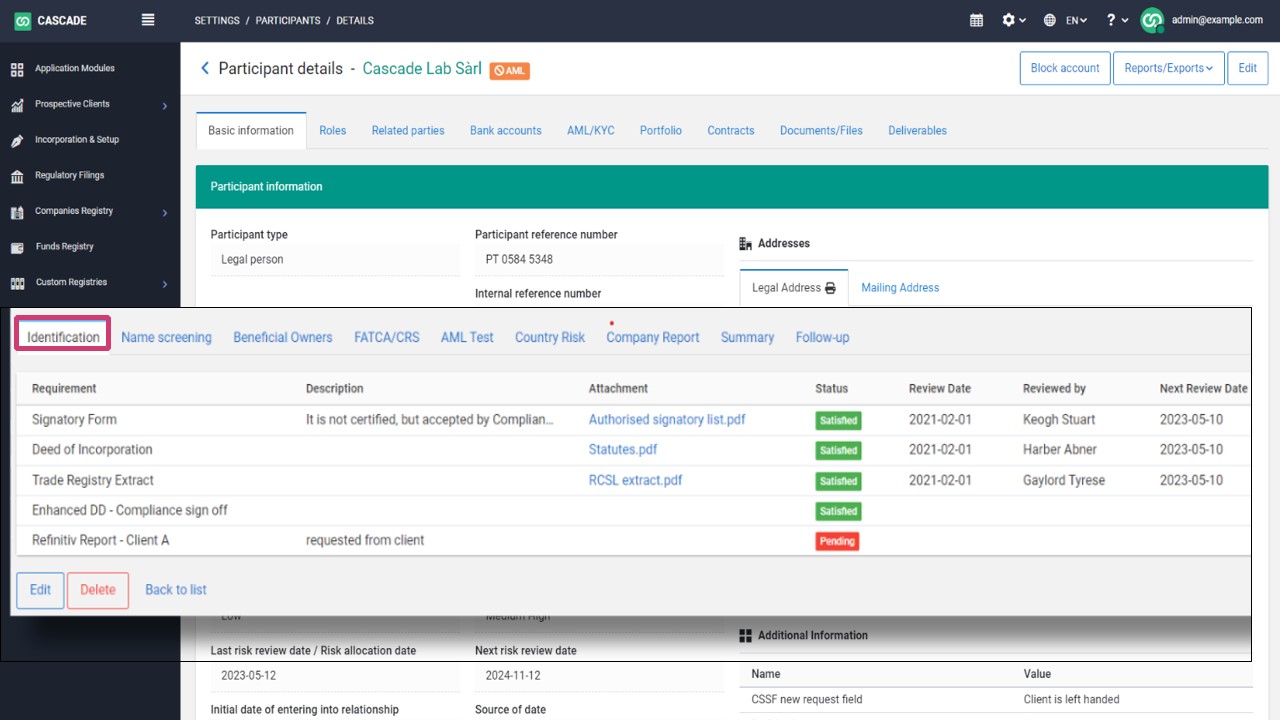
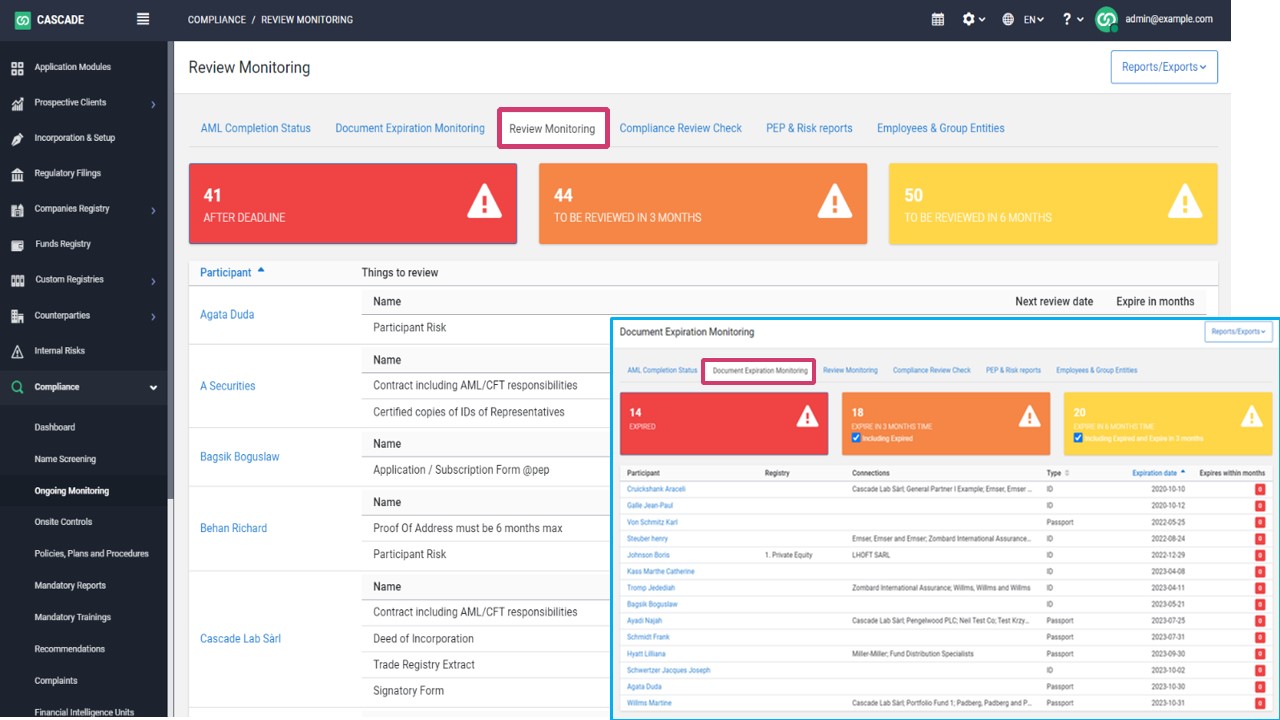
Workflow automation consolidates customer data, screening results, and due diligence evidence into a single audit trail. Alert management engines flag KPI variances in real time. Reporting dashboards give compliance teams and boards instant visibility into performance trends.
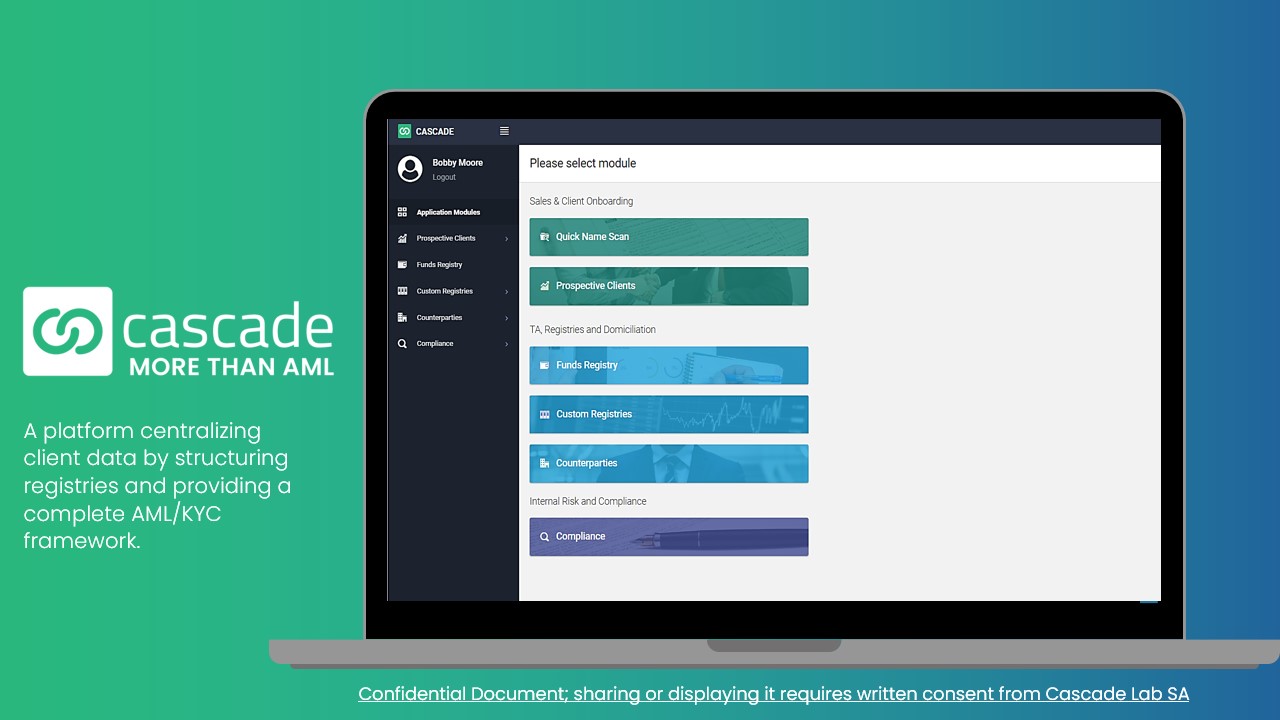
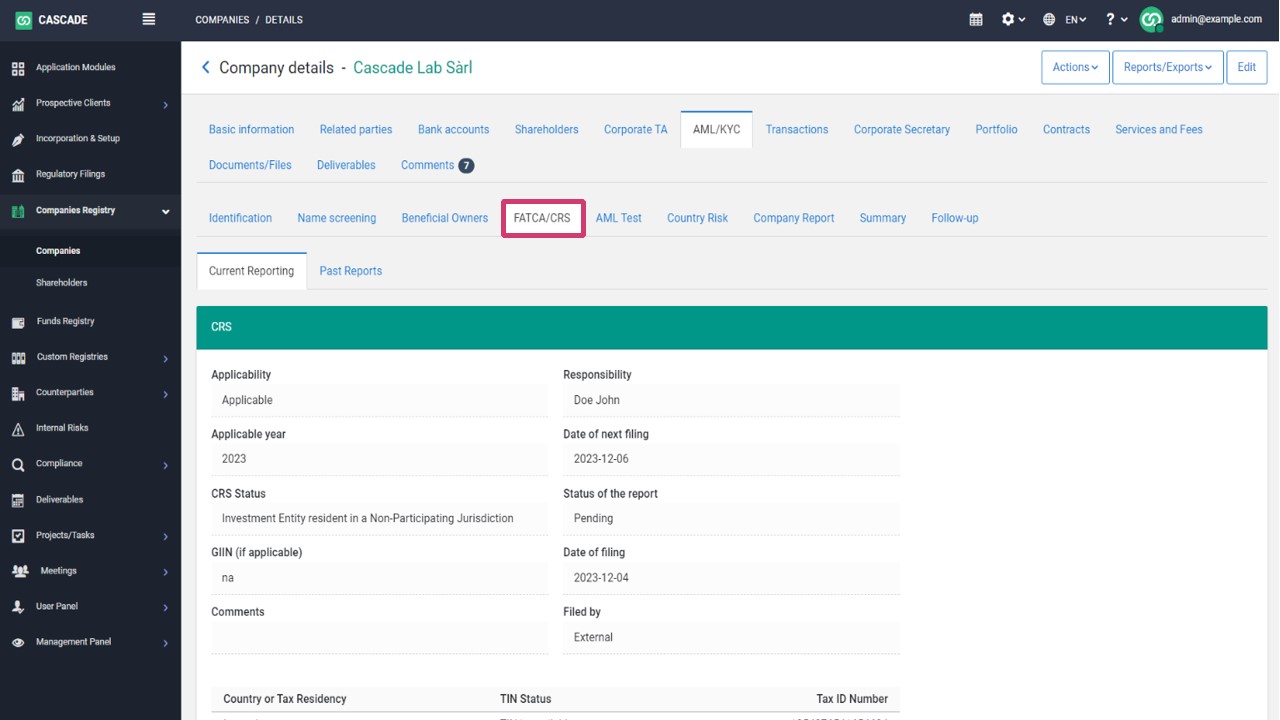
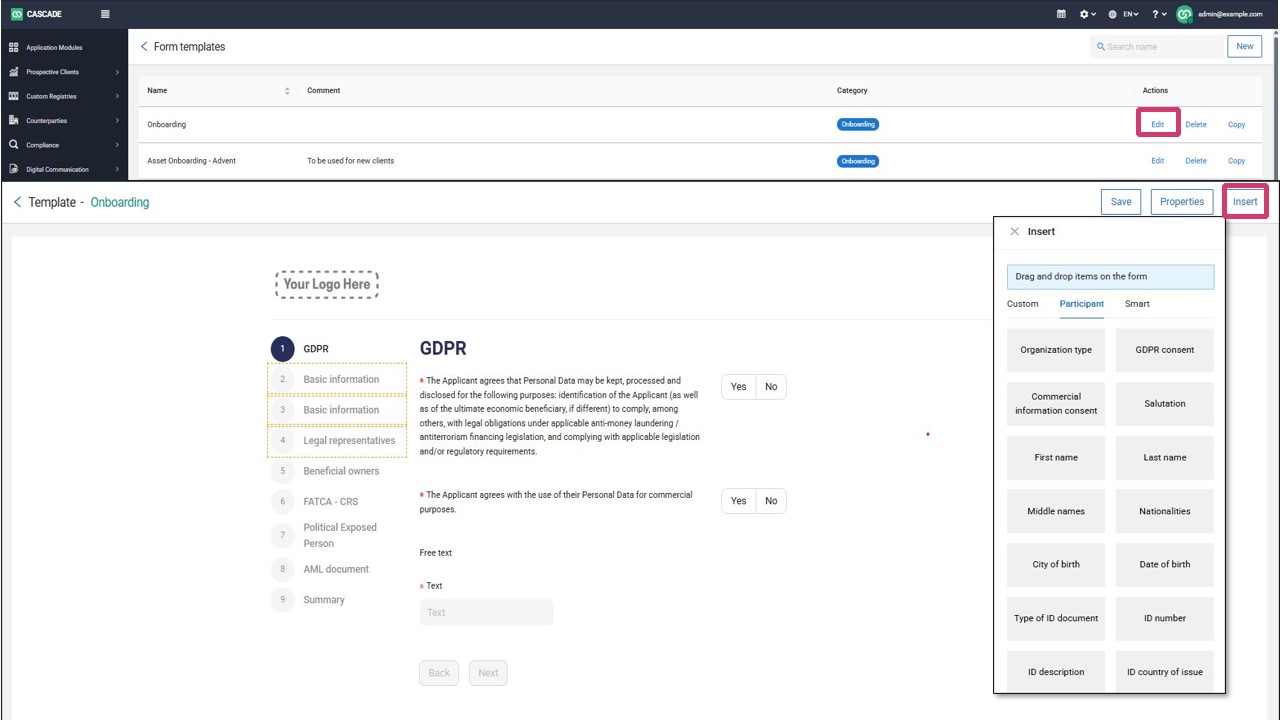
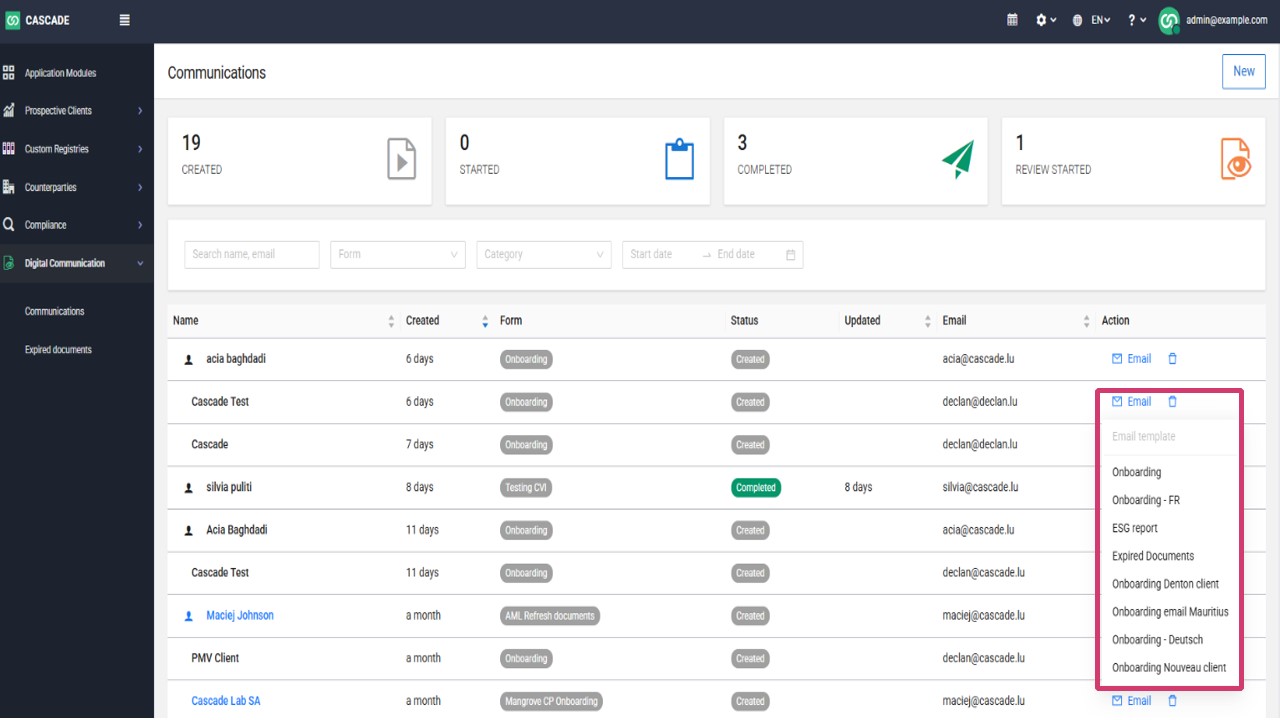
Cascade brings onboarding, screening, and ongoing monitoring workflows into one platform, making KPI data collection transparent and audit-ready.
Frequently asked questions
What is the right AML KPI target for onboarding completion time?
Most Irish fund administrators target 95% of onboarding complete within 10 business days. Targets below 80% indicate process bottlenecks; targets above 98% may be impractical. Base your target on historical data and resource constraints.
How often should we review AML KPIs?
Review operationally monthly and report to board governance committees quarterly. Annual review against regulatory guidance ensures targets stay aligned with risk appetite and regulatory expectations.
What is Cascade, and how does it simplify AML/KYC compliance?
Cascade is an AML compliance technology provider focused on helping regulated businesses manage and automate key parts of their anti-money laundering processes. It brings onboarding, client acceptance, risk-based KYC, and ongoing monitoring into a single workflow with clear controls and audit-ready records. Standardizing workflows and centralizing evidence reduce manual admin and make it easier to demonstrate how decisions were made.
Who can benefit from using Cascade?
Any organization meeting AML/KYC obligations, especially where onboarding volumes, complex ownership structures, or higher-risk customers create pressure. It fits regulated financial services firms, fintechs, wealth managers, law firms, and professional services firms.
How does Cascade ensure data security and regulatory compliance?
Cascade’s AML Software is designed to support secure handling of AML data and compliance workflows, with controls for access, documentation, auditability, and regulatory oversight. Specific security certifications or controls should be verified against Cascade’s current technical and compliance documentation.
How can I get started with Cascade?
Book a discovery call to map your current AML/KYC workflow and pain points, then get a tailored demo with our sales team to discuss implementation timelines. Get started here.
Explore Cascade’s AML KPI capabilities
Fund administrators managing AML performance across multiple teams and geographies often struggle with manual data collection and fragmented reporting. Technology that centralizes onboarding, screening, and ongoing monitoring workflows and captures all decisions in a single audit trail makes KPI tracking transparent and defensible.
Explore Cascade’s capabilities to see how you can embed AML KPI governance into your compliance workflow.
Disclaimer
This article is for general information only and based on publicly available sources and regulatory guidance current as of the publication date. AML rules, fund administrator responsibilities, and technology capabilities can change. Always verify requirements with the Central Bank of Ireland and seek legal or compliance counsel before implementing new AML controls or vendor solutions.


 English
 English (Australia)
 English (UK)