


KYC API Integration in Luxembourg: Building a Connected AML/KYC Workflow
When compliance teams search for KYC API integration, they are often trying to solve a broader problem: how to connect customer data, due diligence, risk assessment, document collection and ongoing monitoring without creating fragmented compliance processes.
An API can be one way of connecting separate technology systems. It is not, however, a regulatory requirement, nor is it the only way to create an efficient KYC process.
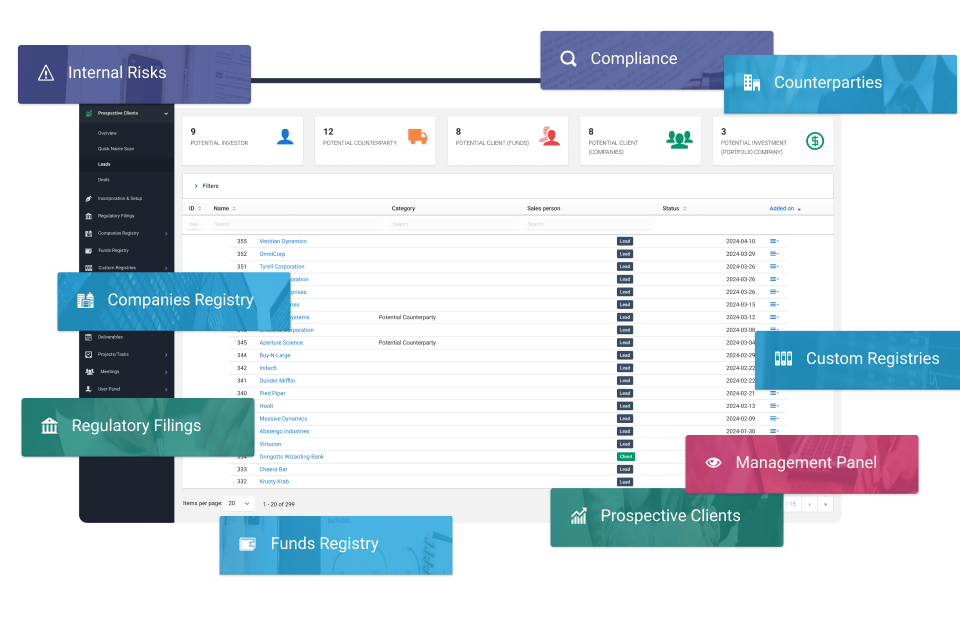
Cascade does not offer KYC API integration. Instead, Cascade’s core AML Software / SaaS Platform is designed to centralise AML/KYC activities within a structured compliance environment. Client and counterparty records, risk-based workflows and ongoing compliance activities can therefore be managed within the platform rather than relying on an API to connect a collection of separate KYC tools. Cascade currently describes its platform as supporting structured registries, risk-based workflows, transaction monitoring and live file status.
For Luxembourg organisations, the underlying objective should be clear: technology should support a controlled, risk-based and well-documented customer due diligence process.
What Does KYC API Integration Mean?
A KYC API is a technical interface that allows one software application to exchange information with another.
For example, an organisation building its own customer onboarding environment might use APIs to send customer information to different identity verification, data or compliance services and return the results to its internal system.
That architecture can be appropriate for organisations with:
- proprietary onboarding applications
- dedicated development resources
- complex technology stacks
- a requirement for automated system-to-system data exchange
- multiple specialised compliance providers
But KYC integration is broader than API integration.
From a compliance perspective, the more important question is whether the organisation can maintain a reliable flow of information from initial onboarding through customer due diligence, risk assessment, approval, monitoring and periodic review.
A disconnected process can remain inefficient even when several APIs are involved. Conversely, a centralised AML/KYC platform can provide a connected workflow without requiring a firm to build its compliance process around APIs.
KYC Integration Without an API
For many compliance teams, integration is primarily an operational challenge rather than a software-development project.
Client information may arrive by email, documents may sit in shared drives, ownership information may be recorded in spreadsheets, and risk assessments may be managed separately from the underlying KYC file. The result can be duplicated work and a more difficult audit trail.
A centralised approach brings these elements together.
Cascade’s AML Software is the core product. Cascade starts with centralised registries for clients, companies, counterparties and beneficial owners alongside risk-based AML/KYC workflows and ongoing monitoring processes.
This approach is different from offering an API that developers embed into another application. Instead of connecting multiple compliance components through technical interfaces, the objective is to manage the relevant AML/KYC information and decisions within a structured platform.
What Should a Connected KYC Workflow Cover?
Effective KYC integration should extend beyond the moment a customer is first onboarded.
1. Client and Counterparty Data
A reliable KYC process starts with structured information.
Compliance teams need to understand who the customer is, which individuals or entities are connected to the relationship and, where relevant, who ultimately owns or controls a legal entity.
Structured records can make it easier to keep relationships between clients, counterparties, beneficial owners and other relevant parties visible throughout the customer lifecycle.
FATF standards place customer due diligence and beneficial ownership within the wider framework for preventing money laundering and terrorist financing. The FATF also identifies the risk-based approach as a cornerstone of its Recommendations.
2. Due Diligence Documentation
KYC information rarely consists of data fields alone.
Depending on the relationship and risk profile, an organisation may need to collect identification documents, corporate records, questionnaires and other supporting evidence.
Bridge: Digital Communication for Client Onboarding is available as an add-on to Cascade’s core AML Software platform. With Bridge you can collect securely client data communicate with your customers.
Keeping document collection connected to AML KYC software can reduce the need to manage evidence across unrelated channels.
3. Risk Assessment
KYC should not be treated as the same checklist for every customer.
The CSSF states that professionals under its AML/CFT supervision are expected to implement a risk-based approach, allocating appropriate resources and controls to customers and products presenting higher risks. It also identifies customer due diligence, adequate internal management and cooperation with authorities among relevant professional obligations.
Technology can support that process by helping firms structure risk factors, document assessments and maintain visibility over the resulting customer risk profile.
The decision-making framework itself must still reflect the organisation’s applicable regulatory requirements, policies and risk appetite.
4. Client Acceptance and Compliance Decisions
Collecting KYC information is only useful if it feeds into a controlled decision-making process.
A connected workflow should make it possible for appropriate users to understand:
- what information has been collected
- which checks have been completed
- what risks have been identified
- whether additional due diligence is required
- who reviewed or approved the relationship
- when the relationship needs to be reviewed again
This creates a clearer link between evidence, analysis and the final compliance decision.
5. Ongoing Monitoring and Review
KYC does not finish when onboarding is completed.
Customer circumstances, documents, ownership structures and risk factors can change over time. A well-designed AML/KYC operating model therefore needs a process for keeping relevant information current and triggering reviews when required.
The CSSF’s AML/CFT framework emphasises risk-based supervision and customer due diligence obligations for professionals subject to its supervision.
For organisations designing their technology stack, this means considering the full lifecycle rather than focusing exclusively on the initial customer verification event.
6. Evidence and Auditability
KYC technology should also help compliance teams demonstrate what happened.
A strong process should make it possible to reconstruct the relevant compliance activity, including the information considered, the decisions made and the people responsible.
This is particularly important where several teams contribute to client onboarding and ongoing monitoring. Centralising the workflow can help avoid an evidence trail spread across spreadsheets, inboxes and disconnected systems.
Luxembourg Regulatory Context for KYC Workflows
Luxembourg professionals within the relevant scope operate under the Law of 12 November 2004 on the fight against money laundering and terrorist financing, together with applicable sector-specific rules and CSSF requirements. The CSSF maintains the consolidated version of the law and updated it most recently on 8 August 2026.
The CSSF specifically highlights customer due diligence, internal management and a risk-based approach within its AML/CFT supervisory framework.
The European regulatory environment is also evolving. Regulation (EU) 2024/1624, the EU Anti-Money Laundering Regulation or AMLR, forms part of the EU’s new AML/CFT framework and will generally apply from 10 July 2027.
For compliance and technology teams, this reinforces the importance of building processes that can be reviewed and adapted as legal and regulatory requirements develop.
Technology alone does not establish compliance. Configuration, governance, procedures, staff responsibilities and appropriate human judgement remain essential.
KYC Workflow Priorities by Industry
The appropriate KYC operating model will depend on the organisation’s activities, customers and regulatory status.
Asset Managers and Investment Fund Professionals
Asset managers, management companies and other investment-sector professionals may need to manage due diligence across investors, counterparties, structures and beneficial owners.
FATF guidance for the securities sector emphasises understanding customer relationships and applying due diligence in proportion to relevant risks. The CSSF has also highlighted the importance of the risk-based approach within Luxembourg’s securities-sector AML/CFT framework.
Corporate and Fiduciary Service Providers
Complex legal structures can make ownership and relationship information particularly important.
FATF guidance for trust and company service providers emphasises initial and ongoing client due diligence, beneficial ownership information and measures proportionate to ML/TF risk.
Structured records can therefore be especially valuable where several companies, individuals and ownership relationships form part of the same client file.
Law Firms
Where legal professionals fall within applicable AML/CFT obligations for relevant activities, customer due diligence needs to reflect the nature of the work and associated risks.
FATF guidance for legal professionals highlights risk assessment together with initial and ongoing client due diligence as key components of the risk-based approach.
Wealth Management
Wealth management relationships can involve multiple individuals, entities, ownership interests and jurisdictions.
A connected AML/KYC workflow can help teams maintain structured information across these relationships while applying the organisation’s own risk-based procedures.
The precise obligations applicable to any organisation should always be assessed against its legal status, services, customer base and jurisdiction.
A Practical Approach to Improving KYC Integration
Organisations do not need to begin with a technology decision. A more useful starting point is to map the compliance process itself.
Step 1: Map the Existing KYC Workflow
Document where customer information originates, where it is stored, who reviews it and where decisions are recorded.
Look specifically for manual transfers, duplicated records and information that sits outside the main compliance file.
Step 2: Define the Authoritative Client Record
Determine where your organisation expects compliance teams to find the current customer, beneficial ownership and risk information.
Creating a reliable central record can be more valuable than adding another technical connection between fragmented systems.
Step 3: Connect Risk Assessment to KYC Evidence
Risk ratings should be supported by the information collected during due diligence.
Avoid treating risk scoring as a separate exercise disconnected from the underlying customer file.
Step 4: Build Ongoing Review Into the Process
Define which events, dates or risk changes should lead to further action.
The objective is to maintain the KYC record throughout the relationship rather than recreating it whenever a review becomes due.
Step 5: Preserve the Decision Trail
Make sure reviewers can understand what information was available at the time of a decision and how the decision was reached.
Step 6: Review Technology Against the Operating Model
Only after the workflow is understood should teams decide whether they require APIs, a centralised AML platform, specialist point solutions or a combination of systems.
The right architecture depends on the organisation. An API is a technical option, not the objective of KYC compliance.
KYC API Integration Versus a Centralised AML Platform
The distinction is useful for organisations evaluating technology.
KYC API integration may suit organisations that:
- are developing proprietary customer-facing systems
- require programmatic exchange between applications
- have internal development and integration resources
- prefer to assemble specialised point solutions
A centralised AML/KYC platform may suit organisations that:
- want client information and compliance activity in one environment
- need structured KYC and risk-based workflows
- want to reduce reliance on spreadsheets and disconnected records
- need clearer visibility across onboarding and ongoing compliance
- prefer to configure workflows rather than build technical integrations
Cascade follows the second model. Its core AML Software (SaaS Platform) focuses on bringing AML/KYC information and compliance workflows together rather than providing KYC API integration.
What About PEP and Sanctions Screening APIs?
PEP and sanctions screening is a more specific technology question and should be considered separately from general KYC workflow integration.
Cascade provides name screening within its AML Software rather than offering a standalone PEP or sanctions screening API. Cascade performs daily name screening using LSEG World-Check, Dow Jones and Acuris Risk Intelligence.
Frequently Asked Questions
Does Cascade offer KYC API integration?
No. Cascade does not offer KYC API integration. Cascade provides a core AML Software designed to centralise AML/KYC information, risk-based processes and ongoing compliance workflows.
Do you need an API to integrate KYC processes?
No. APIs can connect separate applications, but organisations can also create connected KYC processes by centralising relevant client information, risk assessments, documents and compliance activity within an AML/KYC platform.
Is an API required for KYC compliance in Luxembourg?
No specific technology architecture is prescribed simply because an organisation is subject to KYC obligations. Luxembourg AML/CFT requirements focus on obligations such as customer due diligence and risk-based controls rather than requiring firms to use an API. Organisations must determine how best to meet the requirements applicable to their activities.
How is this different from a PEP sanctions screening API?
KYC workflow integration concerns the broader lifecycle of customer information, due diligence, risk assessment and ongoing review. A PEP or sanctions screening API is a specific technical method for sending names to a screening service and receiving potential match information. Cascade’s dedicated PEP and sanctions screening resource explains this distinction in more detail.
Can Cascade support digital client data collection?
Cascade offers the Bridge: Digital Communication as an add-on module requiring the core AML Software platform. It can support secure digital collection of client information and documents as part of the wider AML/KYC workflow.
Related Reading
- Cascade AML Software: overview of the core AML Software.
- PEP and Sanctions Screening API: how screening APIs differ from integrated AML screening.
- Automated Treatment of Name Screening Alerts: Cascade’s add-on module for the treatment and documentation of name-screening alerts. This add-on requires the core AML Software platform.
- CSSF AML/CFT Framework: official Luxembourg regulatory information on AML/CFT supervision and obligations.
- EU Anti-Money Laundering Regulation: Regulation (EU) 2024/1624.
Explore Cascade’s AML/KYC Capabilities
Improving KYC integration does not necessarily mean adding another API.
For organisations that want to structure client information, risk assessment and ongoing AML/KYC activities within one compliance environment, explore Cascade’s AML Software and see how a centralised approach could fit your operating model.
Specific regulatory requirements vary by jurisdiction, sector and business model. This content is not legal advice. Organisations should consult a qualified AML professional in Luxembourg, or in the jurisdiction relevant to their activities, when assessing their compliance obligations.
Disclaimer: This article is for general information only and based on publicly available sources at the time of writing. We’ve done our best to make it accurate and useful, but AML rules and business needs can change. Always double-check key details and speak with a qualified expert before making compliance or vendor decisions.



 English
 English (Australia)
 English (UK)




























