Setting the right monitoring frequency
This guide explains how to build a risk review cadence policy for wealth management operations in the United States. You’ll learn how to set monitoring frequencies based on customer risk tier, what regulators expect, and how to implement a risk review cadence policy for Wealth Management of USA that scales across your book of business. By the end, you’ll have a practical, defensible framework for determining when and how often you reassess customer and beneficial ownership risk.
Introduction
US wealth managers face mounting pressure to prove they’re actively monitoring customer risk, not just conducting initial onboarding. The SEC, FinCEN, and the OCC all expect firms to set clear risk review cadence policies and follow them. A robust risk review cadence policy for Wealth Management USA demonstrates to regulators that you’re managing financial crime exposure deliberately and with documented governance.
Without a clear policy, wealth teams default to annual reviews or ad hoc reassessments. With one, you align monitoring frequency to actual risk and regulatory expectations. This guide walks you through both.
What is a risk review cadence policy for wealth management?
A risk review cadence policy is a written governance framework that specifies how often you will reassess customer and beneficial ownership risk. For wealth management, cadence varies by customer risk tier: high-risk customers may require a quarterly review, standard-risk customers an annual review, and low-risk customers one every three years. The policy documents the rationale, the review triggers, and the responsible parties. It converts abstract compliance intent into a calendar and a checklist.
The USA must account for high-net-worth complexity, cross-border beneficial ownership, and the evolving regulatory expectations around ongoing customer due diligence (CDD).
Why risk review cadence matters for US wealth managers
Regulators see weak or absent cadence policies as a red flag. They indicate the firm may not be monitoring risk actively. The SEC’s exam findings from 2023 repeatedly cited “inadequate or undocumented monitoring policies” as a compliance deficiency. FinCEN’s guidance on beneficial ownership updates also requires firms to maintain a reasonable cadence for verification and updates.
Beyond regulation, cadence disciplines your compliance team. It prevents monitoring fatigue and ensures you focus resources on the customers who need it most. It also creates a defensible audit trail: you can show examiners exactly when each customer was reviewed and why.
Regulatory expectations for US wealth managers
The SEC’s Rule 17j-1 and Regulation S-P require wealth managers to implement written policies governing customer supervision and due diligence. FinCEN‘s Customer Due Diligence rule and the beneficial ownership guidance expect firms to maintain and update CDD information at intervals appropriate to customer risk. The OCC‘s Comptroller’s Handbook on AML/CFT supervision reinforces that cadence must be proportionate, documented, and followed consistently.
A risk review cadence policy for Wealth Management USA should reference these expectations and explain how your firm’s policy meets them.
Building your risk review cadence policy
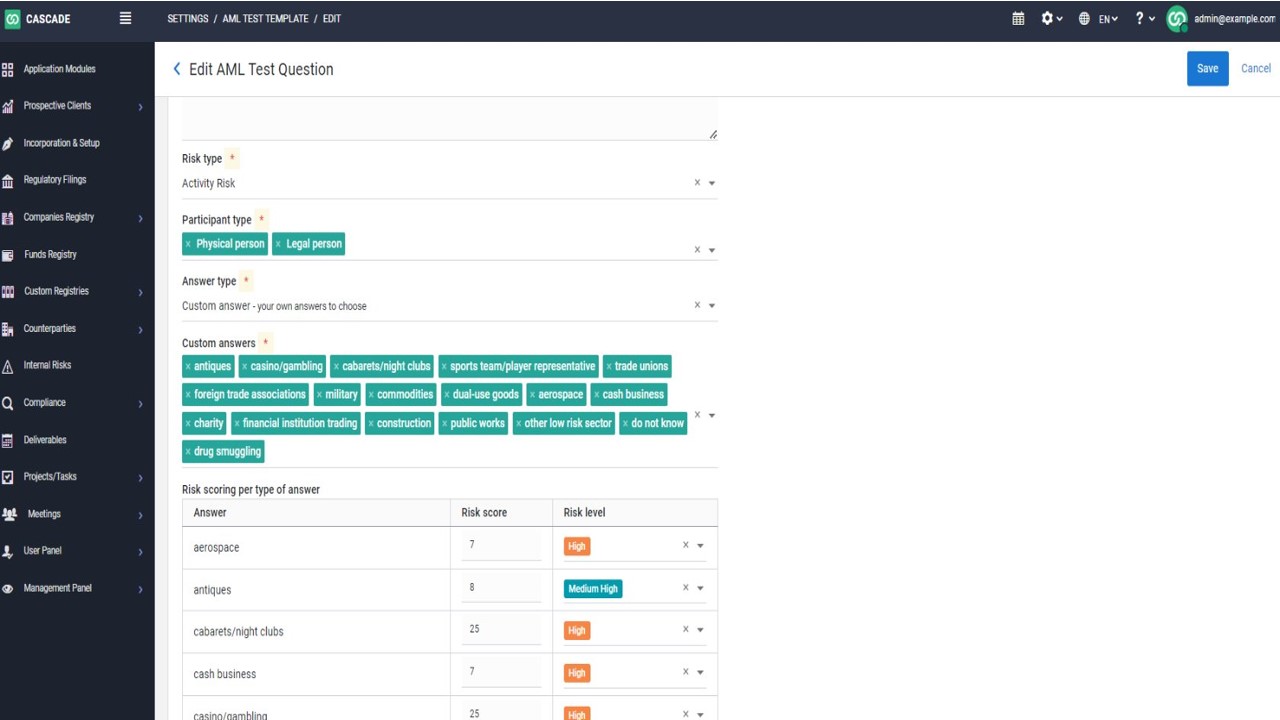
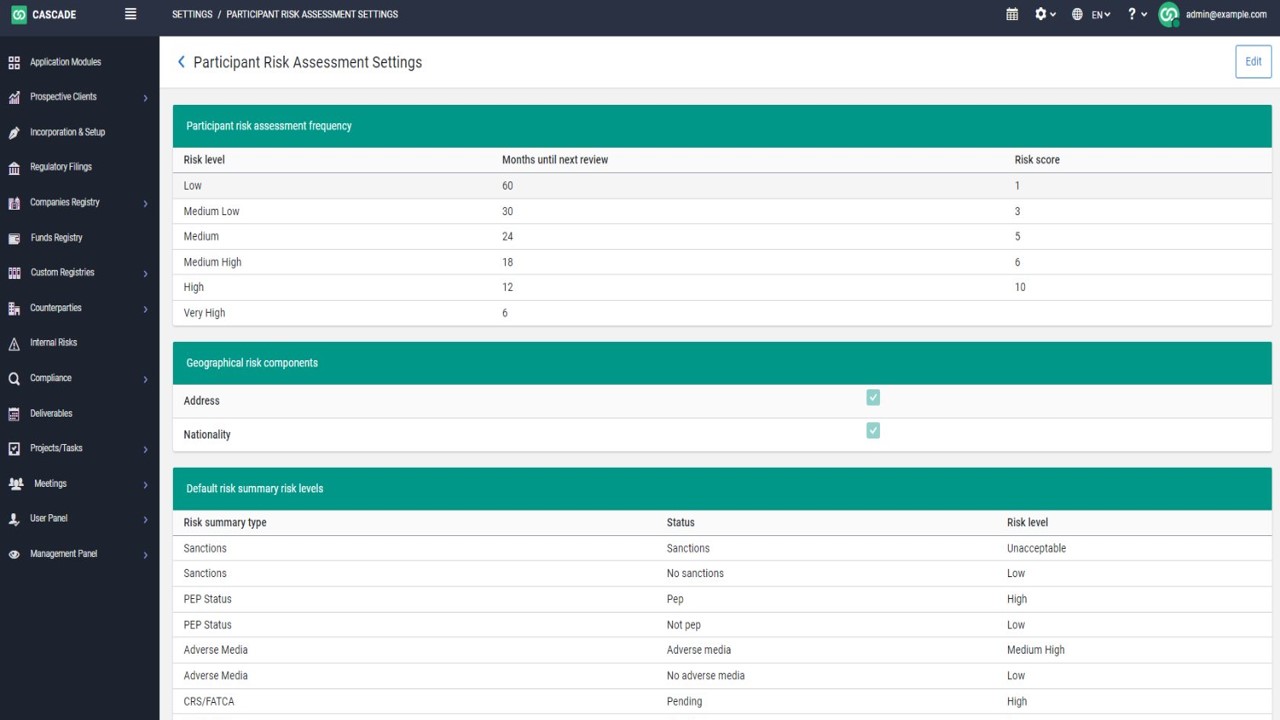
Start by defining your risk tiers: high, medium, and low. Map customer attributes to tiers (AUM, geography, beneficial ownership complexity, and regulatory status). Assign review frequencies: high-risk customers quarterly or semi-annually; medium-risk annually; low-risk every 24-36 months. Document the triggers for out-of-cadence review (suspicious activity, media alerts, sanctions hits, and significant asset movement). Assign ownership: typically the relationship manager or a centralized compliance team. Obtain board and senior management sign-off. Review and update annually.
Sample risk review cadence matrix
| Customer Risk Tier | Review Frequency | Review Components | Escalation Trigger |
|---|---|---|---|
| High | Quarterly | Full CDD, beneficial ownership, source of wealth, media scan | Any risk indicator |
| Medium | Annual | CDD refresh, beneficial ownership update, transaction review | Threshold breach or new information |
| Low | Every 36 months | Simplified CDD update, beneficial ownership confirmation | Material change or event |
Common cadence mistakes
Wealth managers often set cadences too infrequently (e.g., every five years for low-risk), creating compliance gaps. They apply flat cadences across all customers regardless of risk. They fail to document the rationale for their tiers and frequencies. They lack systematic tracking, leading to reviews being missed. They also fail to adjust cadence when customer risk changes.
Best practices
Base tiers and frequencies on documented risk appetite and regulatory expectations. Use a risk-based approach: stricter cadence for complex or higher-risk profiles. Document the policy in writing with examples. Integrate cadence into your compliance calendar and monitoring systems. Track completion and investigate variances. Review and update annually. Train your relationship managers on policy requirements.
How technology can help
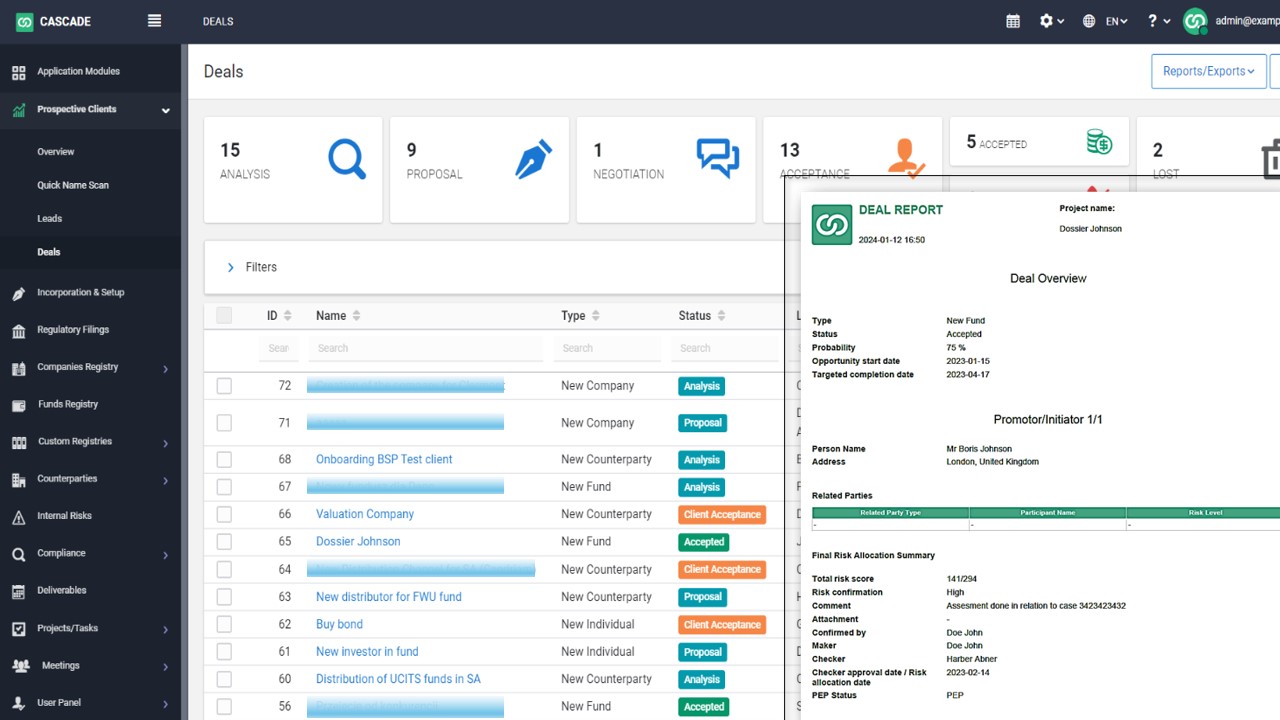
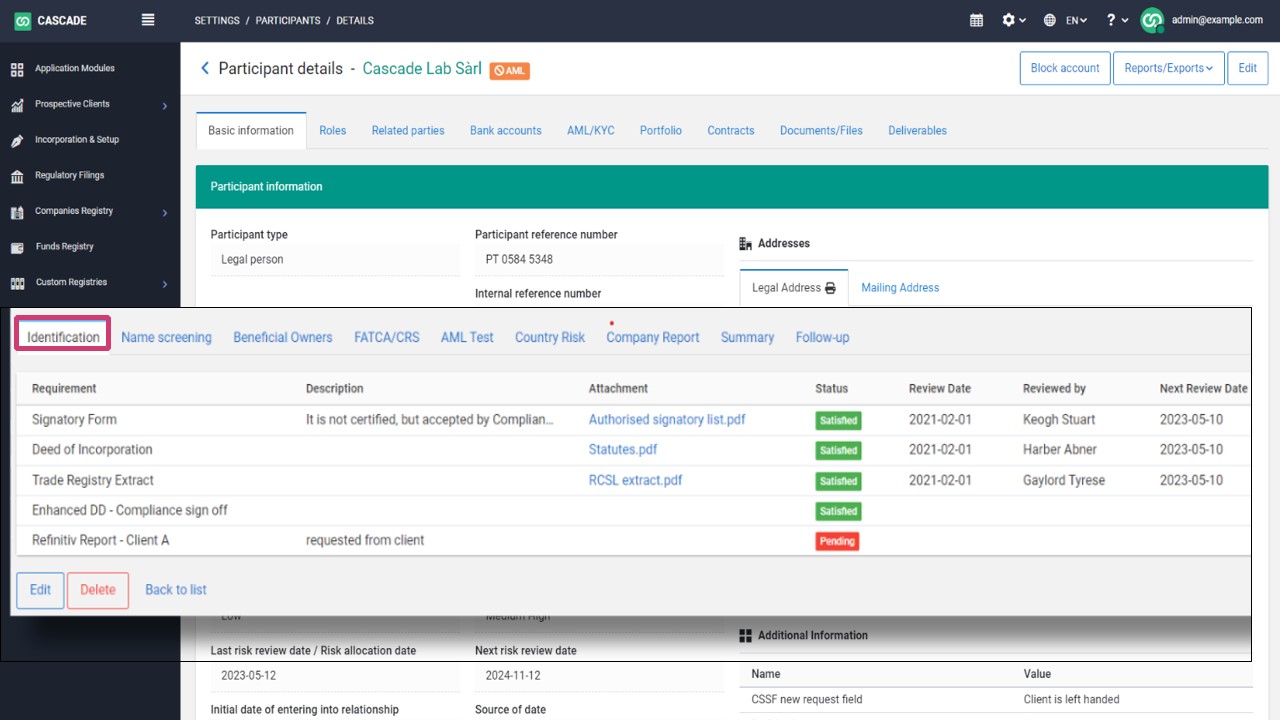
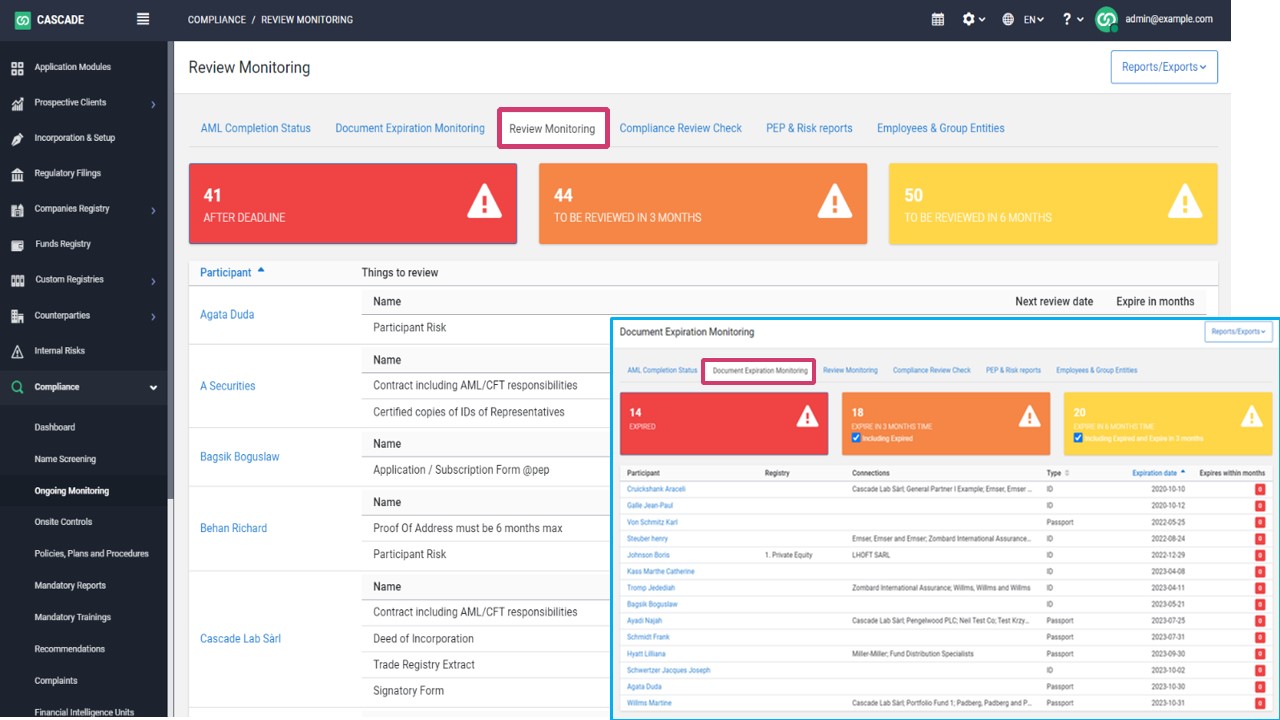
Workflow automation flags when a customer’s review date is approaching. Alert management engines can monitor customer activity between reviews and flag changes warranting out-of-cadence reassessment. Centralized tracking and audit trails make it easy to demonstrate compliance to examiners.
Cascade consolidates customer profiles, due diligence history, and review schedules into a single workflow, helping ensure cadences are set, tracked, and completed on time.
Frequently asked questions
How do I decide on cadence frequencies?
Start with regulatory guidance and peer practice, then adjust based on your book composition. If 60% of your clients are high-complexity international structures, your high-risk cadence may need to be quarterly rather than annual. Document the rationale.
What triggers an out-of-cadence review?
Suspicious activity, media alerts, significant asset movement, sanctions or PEP list hits, changes in beneficial ownership, or regulatory inquiries. Document these triggers in your policy.
What is Cascade, and how does it simplify AML/KYC compliance?
Cascade is an AML compliance technology provider focused on helping regulated businesses manage and automate key parts of their anti-money laundering processes. It brings onboarding, client acceptance, risk-based KYC, and ongoing monitoring into a single workflow with clear controls and audit-ready records. Standardizing workflows and centralizing evidence reduce manual admin and make it easier to demonstrate how decisions were made.
Who can benefit from using Cascade?
Any organization meeting AML/KYC obligations, especially where onboarding volumes, complex ownership structures, or higher-risk customers create pressure. It fits regulated financial services firms, fintechs, wealth managers, law firms, and professional services firms.
How does Cascade ensure data security and regulatory compliance?
Cascade supports data security and regulatory compliance through role-based access, secure document handling, audit trails, controlled workflows, and configurable retention practices.
How can I get started with Cascade?
Book a discovery call to map your current AML/KYC workflow and pain points, then get a tailored demo with our sales team to discuss implementation timelines. Get started here.
Explore Cascade’s risk review cadence capabilities
Wealth managers juggling hundreds or thousands of customer records often rely on spreadsheets or manual calendars to track review cadences. When cadences slip or when customer risk changes between scheduled reviews, compliance teams have no way to flag the gap. A centralized workflow platform that automates cadence scheduling, flags approaching review dates, and routes risk reassessment tasks ensures your risk review cadence policy for wealth management in the USA stays current and auditable.
Learn how Cascade can automate your risk review workflow.
Disclaimer
This article is for general information only and based on publicly available regulatory guidance and industry practice current as of the publication date. SEC, FinCEN, and OCC expectations, customer risk classifications, and technology capabilities can change. Always verify current regulatory requirements and consult with your compliance counsel and legal advisors before implementing or updating risk review cadence policies.


 English
 English (Australia)
 English (UK)